Clusterward
Audit & NIS2

NIS2 audit coming up? Your operations already provide the evidence

If you fall under NIS2 or are getting ISO 27001 certified, you have to show who may do what, who did what and how data comes back. Clusterward enforces these rules in Kubernetes operations and records every change – you export the evidence instead of hunting it down.

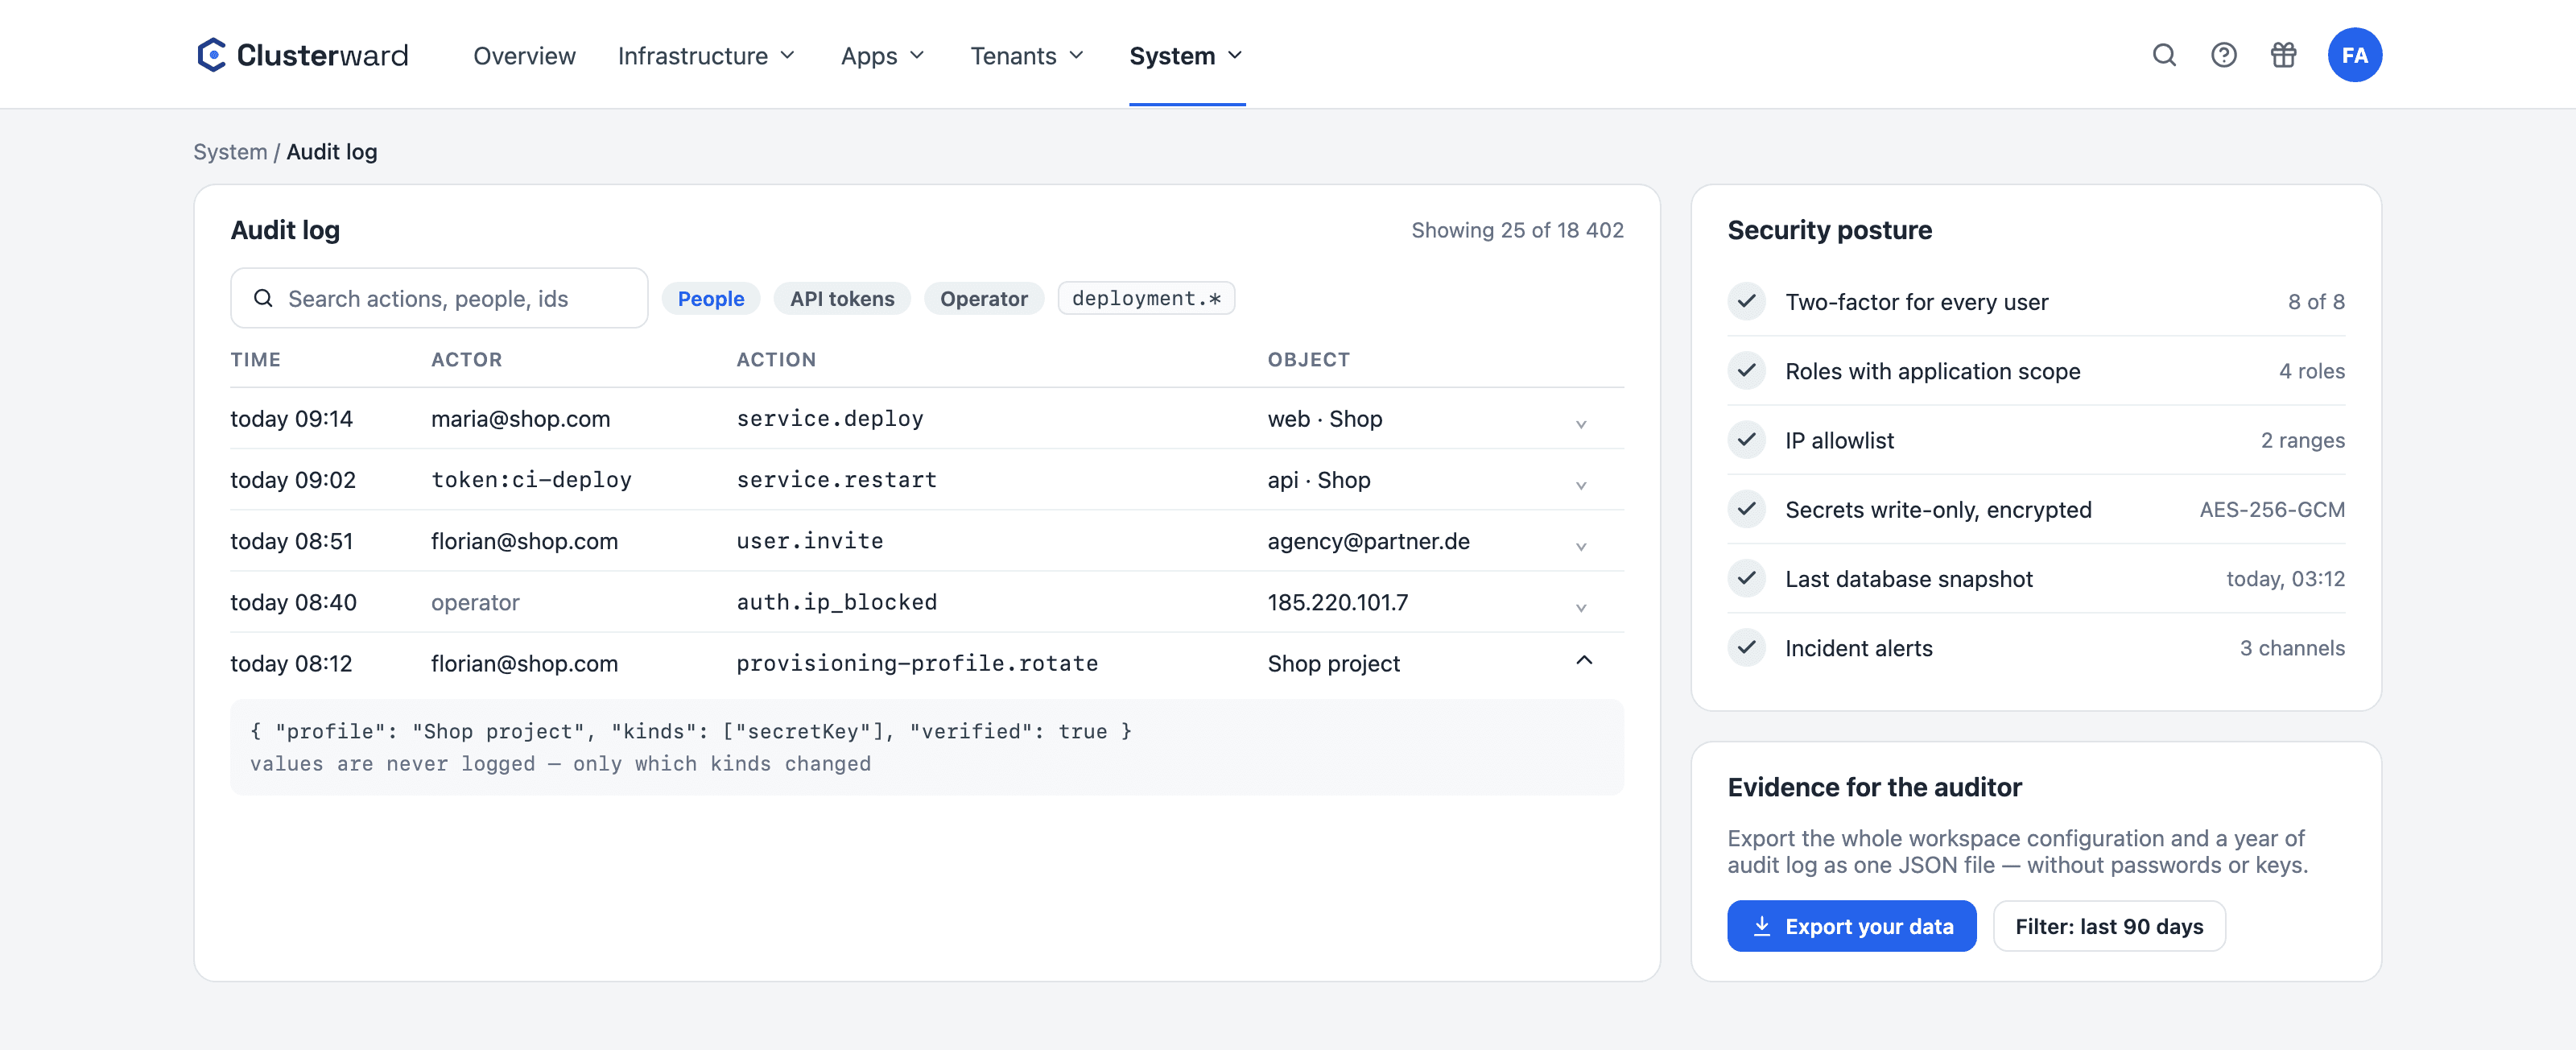
Audit log and security overview in the Clusterward Cockpit
Audit log and evidence in the Clusterward cockpit
Illustration: a simplified view. The product shows more details and options.
In brief

What Clusterward contributes to NIS2 and ISO 27001

Art. 21 of NIS2 requires technical and organizational measures, including access control, multi-factor authentication, encryption, backups and incident handling. Clusterward implements the technical parts for running your applications on Scaleway and logs them. That does not automatically make a company NIS2-compliant – risk analysis, reporting channels and training remain your responsibility – but it makes your Kubernetes operations auditable.

At a glance

Sign-in
Mandatory 2FA for all users, lockout after failed attempts
Permissions
Roles per area, restricted to applications
Log
Every change with the person or API token
Data access
Read-only SQL queries logged with person, text and duration
Secrets
AES-256-GCM encrypted, write-only
Backups
Database snapshots, volume snapshots, export
Location
Scaleway data centers in the EU
How it works

From audit date to evidence

  1. 01

    Set rules

    Set up roles, application scope, IP allowlist and alerts once.

  2. 02

    Work

    Deployments, databases and access run through the cockpit or API tokens.

  3. 03

    Record

    Every change lands in the audit log; secrets never in plain text.

  4. 04

    Prove

    Filter the audit log or export the entire configuration as a file.

What’s included

What evidence your operations provide

Not as a year-end report, but as a property of every action in the cockpit.

Multi-factor for everyone

Every user signs in with a password and a TOTP code, without exception. After failed attempts the account is locked, and sign-ins are rate-limited per address.

Permissions as needed

Roles define per area whether someone may view, operate or manage, and on which applications. An auditor role reads the audit log without being able to change anything.

A complete audit log

Every change with the time, the person or API token and the affected object – filterable by person, action and time range. Secret values never appear in it. Every read-only look into a database through the SQL console is in it too.

Encryption

Credentials and secrets are stored AES-256-GCM encrypted and are never displayed again after saving. Every host gets a TLS certificate.

Backups and recovery

Automatic database snapshots, backups of individual databases, volume snapshots and a return to any earlier version – with confirmation and a log entry.

Spotting incidents

Failed deployments, stuck pods, expiring certificates and changed secrets report in via webhook, Slack, Teams or email.

What changes

Audit preparation with and without Clusterward

Facts

NIS2 Art. 21 and what Clusterward contributes

Guidance, not legal advice: the measures from Art. 21(2) and where operations help.

MeasureWhat Clusterward contributesStays with you
Access controlRoles, application scope, IP allowlistWho gets which role
Multi-factor authenticationTOTP for every user, without exceptionEmployees’ devices
CryptographyEncrypted secrets, TLS for every hostEncryption within the application
Business continuitySnapshots, backups, earlier versions, exportEmergency plan and recovery tests
Incident handlingAlerts and audit log as a trailReporting to authorities and customers
Vulnerabilities and maintenanceKubernetes and add-on updates, hardened podsDependencies in your own code
Supply chainEU provider, your own Scaleway project, your own registryAssessing your service providers
Further reading

How the evidence fits together

Roles, mandatory 2FA, IP allowlist and API tokens are described in Security & access. How databases and volumes come back is covered under Backups & recovery.

Which events raise an alert, and where it goes, is shown under Notifications. Why an EU location matters for your supply chain is explained in Digital sovereignty.

Which questions an auditor asks and which evidence holds up is shown in NIS2 in Kubernetes operations; why Kubernetes Secrets alone are not enough, in Kubernetes Secrets: why Base64 is not encryption.

Related pages

What goes with it

FAQ

Frequently asked questions about audit & NIS2

  • No, no software can do that. NIS2 also requires risk analysis, policies, training and reporting channels. Clusterward implements the technical measures for running your applications on Scaleway and provides the evidence for them – an important, auditable part, but not the whole.

Can’t find your question? Write to us – we usually reply on the same business day.

Ask a question

Your audit questions in the demo

Bring your checklist: we show roles, 2FA, audit log, backups and export on a running environment.